Unprecedented Public Extortion
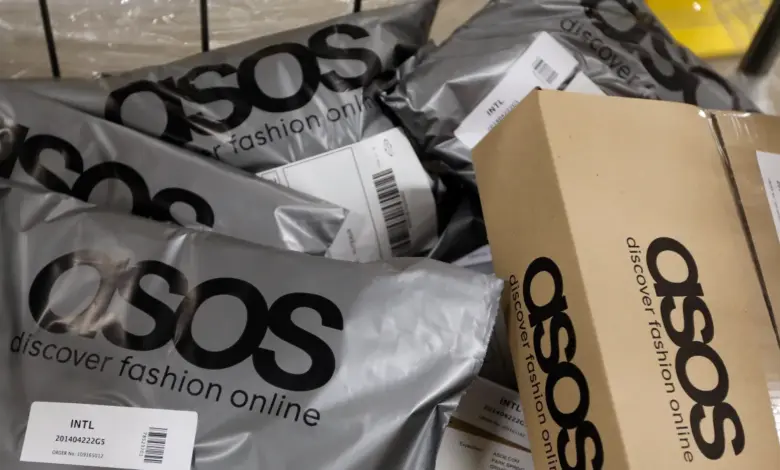
The incident unfolded around 10:00 BST on Tuesday morning when dozens of users reported receiving a push notification from the Asos app. The message was addressed directly to the company’s data protection officer and IT teams, with a headline reading “ASOS HACKED.” The body of the notification stated: “We have fully compromised the Snowflake instance.” Snowflake is a cloud-based data platform used by many enterprises for data warehousing and analytics.
Cybersecurity experts have described the tactic as “brazen” and “deeply serious.” Charlotte Wilson, head of enterprise at cyber-security firm Check Point, noted that hackers rarely inform potential victims’ customers directly; most extortion attempts are conducted in private. By turning the company’s own app into a ransom note, the attackers aimed to maximize pressure on Asos to pay a demand. The notification served as a public warning that data had been accessed, a method that significantly differs from traditional data breach notifications issued by companies after a delay.
Customer Impact and Global Reach
The alert was not limited to the United Kingdom. Users in Australia, France, Sweden, and the Republic of Ireland also reported receiving the same notification, indicating a global impact consistent with Asos’s operational footprint. The British retailer serves approximately 17 million customers annually across more than 150 markets. While the exact number of devices affected remains unclear, the Asos app has been downloaded to Android devices more than 10 million times, according to Google Play Store data.
Asos acknowledged the “unauthorised activity” involving third-party platforms it uses on Tuesday afternoon. In an email sent to customers later that evening, the company apologized and clarified that some “basic personal information” may have been accessed. The retailer emphasized that its core e-commerce functionality remains intact, stating that customers can “shop with confidence” while the investigation continues. The company has not yet informed the UK’s Information Commissioner’s Office (ICO) about any confirmed breach of personal data.
Market Reaction and Security Advice
The public nature of the attack had an immediate impact on the company’s financial standing. Shares in Asos fell by approximately 10% on Tuesday following the disclosure of the incident. The drop reflects investor concern over potential regulatory fines, remediation costs, and reputational damage associated with a high-profile cyberattack.
Security experts have advised users to remain calm but vigilant. Charlotte Wilson from Check Point encouraged concerned customers to change their passwords, avoid clicking on any links provided in the notification, and be cautious of potential follow-up phishing emails or text messages. The incident highlights the growing risk of attackers exploiting third-party services and cloud infrastructure used by major retailers, even if the primary e-commerce platform remains secure.
Asos is currently investigating the scope of the unauthorised activity and the specific third-party platforms involved. The company has not disclosed whether a ransom demand was made or paid, nor has it provided a timeline for completing its internal investigation. The situation remains under review, with no further updates scheduled at this time.