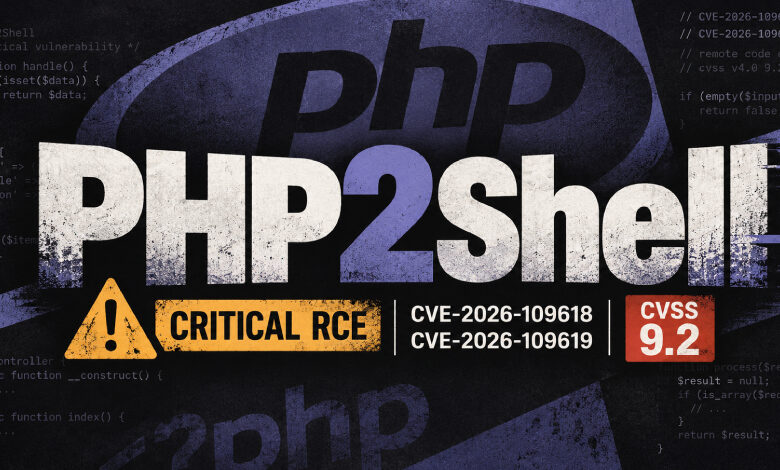
The urgency of the release stems from a leak on the Hacker News platform on October 20, which prematurely disclosed the existence of the flaws, their severity, and two CVE identifiers: CVE-2026-109618 and CVE-2026-109619. The leaked post claimed the vulnerabilities affected all versions from PHP 5 onward and carried a CVSS score of 10.0. However, watchTowr clarified that the 10.0 rating was part of the unauthorized leak, whereas the official vendor rating is 9.2. The claim that versions prior to 8.2 are affected remains unconfirmed by an official vendor advisory, as PHP has stated it will publish the full scope of affected versions alongside the fix.
PHP will only provide fixes for its four currently supported branches: 8.2, 8.3, 8.4, and 8.5. Trackers including Alpine Linux and security researcher Kevin Beaumont expect the fixes to ship as point releases 8.5.12, 8.4.27, 8.3.36, and 8.2.35, respectively, although PHP has not officially confirmed these version numbers. Versions 8.1, 8.0, 7.x, and 5.x are end-of-life and will not receive vendor patches. If the vulnerabilities do extend to these older branches, approximately 884,000 internet-facing hosts running PHP 8.1 or older, as identified by Shodan on October 20, would remain exposed without a direct software update.
As of October 21, no active exploitation has been reported in the wild. Security firm Huntress stated it had not observed exploitation in its partner environments and was unaware of public exploit code. The vulnerabilities are also not listed in the CISA Known Exploited Vulnerabilities catalog. For comparison, a previous PHP flaw, CVE-2024-4577, saw exploit attempts within 24 hours of disclosure. Until the patch is released, PHP has not published a workaround. Organizations are advised to monitor for the official advisory, which will clarify whether the attack requires specific configurations, CGI modes, or authentication, and which part of the PHP engine is involved.
The development of the “PHP2Shell” name comes from independent researchers and is not an official PHP designation. The PHP team emphasized in their notice that they may release the fix earlier than scheduled should details of the vulnerabilities become public or if evidence of active exploitation emerges. Users of end-of-life PHP versions are urged to plan for immediate migration, as these systems will have no vendor-provided mitigation once the full details are published.
One Comment