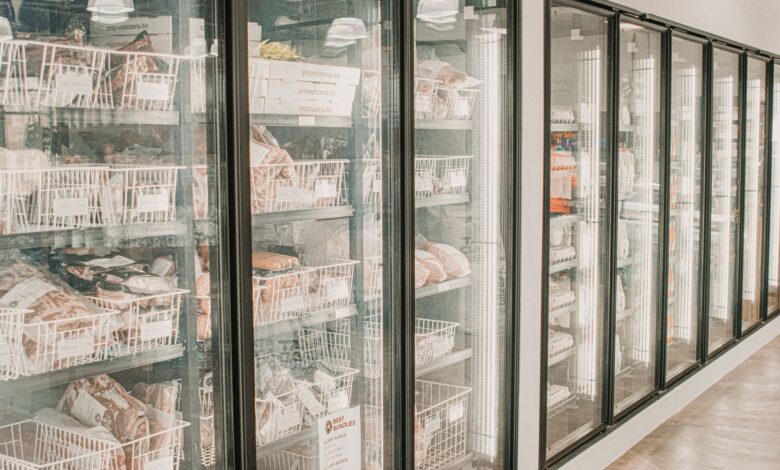
The attack allowed threat actors to seize control of critical infrastructure within retail environments. While the specific retailers involved were not named in the report, the incident underscores a significant vulnerability in the digital management of physical assets in the grocery sector. The compromise of refrigeration systems poses immediate risks to product integrity and supply chain operations, highlighting the intersection of information technology and operational technology in modern retail.
According to the French cyber security agency, the root cause of the breach was not a complex zero-day exploit or advanced persistent threat, but rather “basic security flaws.” The agency explicitly cited a lack of protection and weak passwords as the primary factors that facilitated the criminal intrusion. This distinction is critical for industry stakeholders, as it suggests that standard, low-cost security hygiene practices could have prevented the incident. The reliance on easily guessable credentials for systems that control physical hardware represents a persistent risk vector in industries where legacy systems or internet-of-things (IoT) devices are integrated without robust authentication protocols.
This incident serves as a stark reminder of the security gap in connected physical infrastructure. In many retail and industrial settings, devices such as smart fridges, freezers, and HVAC systems are often connected to the internet for remote monitoring and management. When these devices are not segmented from the main network or protected by strong, unique passwords, they become entry points for larger attacks. The French agency’s commentary implies that the retailers failed to implement basic access controls, allowing unauthorized users to manipulate system settings.
There is no indication in the source material that this was part of a coordinated, multi-vector campaign or that other types of data, such as customer payment information, were compromised. The focus remains strictly on the operational control of the refrigeration units. The incident does not specify the duration of the compromise or the extent of the physical damage, if any, caused by the manipulation of the systems. However, the potential for financial loss through spoiled inventory and operational disruption is significant.
Regulatory and industry bodies are likely to use this case to reinforce the need for stricter security standards in the retail sector. The emphasis on “basic” flaws suggests that existing guidelines for securing industrial control systems (ICS) and IoT devices were not followed. Companies are expected to review their password policies, implement multi-factor authentication where feasible, and ensure that critical infrastructure devices are properly firewalled and monitored. The incident serves as a cautionary example of how neglecting fundamental security principles can lead to tangible operational risks.
As of the publication of this report, no specific patch deadline, regulatory step, or company milestone has been announced in response to this specific incident. The focus of the available information is on the cause of the breach and the broader implications for security practices in retail infrastructure.