The primary vessel under scrutiny was the VL Prosperity, a Liberian-flagged supertanker measuring 1,093 feet in length. At the time of the incident, the ship was transporting approximately 2.3 million barrels of crude oil from Egypt’s Sidi Kerir terminal to Galveston, Texas. Vessel tracking data indicates the ship departed on August 1 and slowed its speed near the Strait of Gibraltar around August 7, a period that coincides with the reported cyber intrusion. A second vessel, the LPG carrier Kohaku, was also targeted while transiting the same waterway on its way to a different Texas port for loading operations.
The technical details of the breach, as described by Iranian state media and corroborated by cybersecurity experts, suggest a sophisticated attack on the ship’s operational technology (OT) systems. Reports indicate that hackers gained access to the engine room, specifically interfering with engine cooling flows, increasing engine speed, and disrupting fuel and engine-oil systems. These actions resulted in a complete loss of communications for nearly 30 hours. Rob Lee, CEO of industrial cybersecurity firm Dragos, noted that the reported technical behaviors were “spot on” and highly realistic for the type of systems found on modern tankers, though he emphasized that the identity of the perpetrator remains unconfirmed by U.S. authorities.
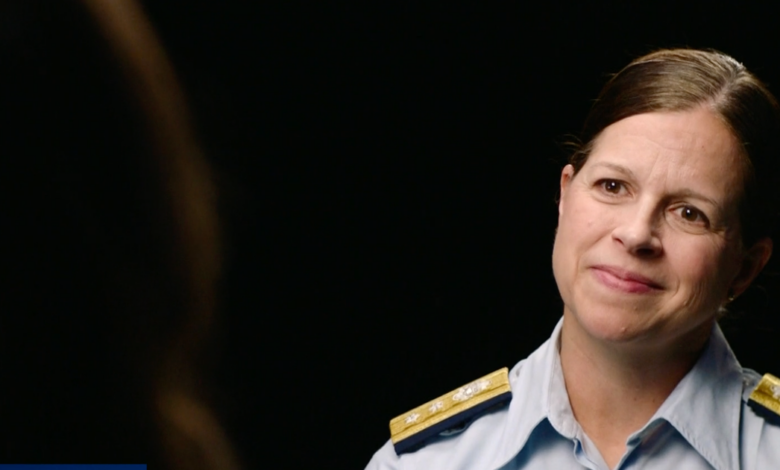
“The real thing we’re concerned about is those IT systems being connected to other systems on the ship that control propulsion, navigation and other systems that are critical to the safety of that vessel,” said Rear Adm. Amy Grable, commander of U.S. Coast Guard Cyber Command.
Grable explained that the core danger lies in the interconnectivity of modern ship systems. While the initial breach may have occurred in standard information technology networks, the ability to pivot to control engineering, propulsion, or navigation systems poses an immediate physical threat. If a malicious actor can gain control of these critical functions, the crew could lose command of the vessel, potentially leading to collisions, grounding, or catastrophic mechanical failure. The Coast Guard’s Cyber Protection Team, which has conducted between 40 and 50 such missions in the past year, was deployed to hunt for malware and assess the extent of the compromise.
U.S. officials are actively investigating whether these two separate incidents were coordinated and whether they were orchestrated by Iran or an Iran-aligned state actor. While no organization has publicly claimed responsibility, the timing and location of the attacks have raised alarms among Washington policymakers. Officials worry that Tehran may be seeking to expand its offensive capabilities beyond the Middle East’s existing maritime flashpoints, targeting the global energy supply chain more broadly. The VL Prosperity’s manager confirmed that U.S. authorities conducted a thorough cybersecurity inspection and that the vessel was subsequently cleared for normal operations.
The incident highlights a persistent vulnerability in the maritime industry: the integration of consumer-grade IT systems with critical OT infrastructure. As ships become more digitized, the attack surface for potential adversaries expands. The investigation continues to determine if the attackers successfully exfiltrated data or merely disrupted operations. For now, the VL Prosperity and the Kohaku have resumed their transatlantic journeys, but the episode serves as a stark reminder that the digital integrity of a supertanker is just as critical to global security as the physical integrity of its hull.