The incident emerged late on Friday, November 6, when several pages on Bank Rakyat’s corporate web portal were briefly defaced. A threat actor operating under the handle “Marlanwg” left a prominent notice on the site claiming to have conducted a “security assessment” and asserting unauthorized access to the bank’s internal network infrastructure. The attacker’s message stated: “Marlanwg is here. We have successfully accessed the internal infrastructure and retrieved a sample of your data to verify the extent of the breach.” The actor also requested contact via the encrypted messaging app Session.
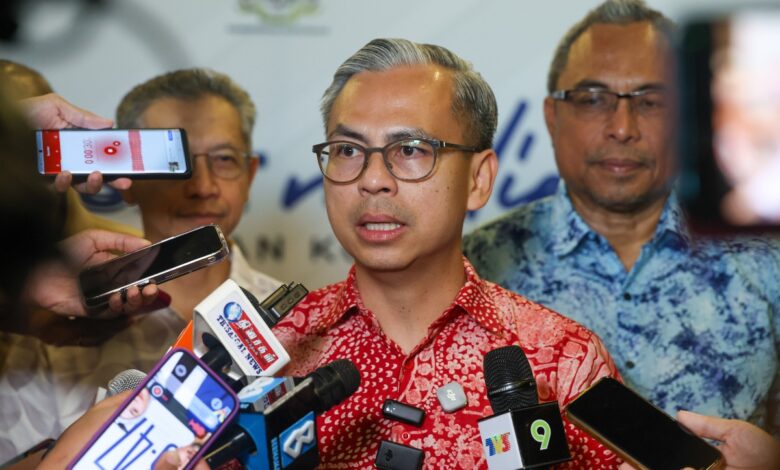
However, Fahmi clarified that the hacking attempts detected so far had not resulted in data theft or affected the country’s online banking operations. “In the latest development, Bank Rakyat reported that its third-party-managed website had been hacked, but the incident was limited to web defacement and the website had been taken over,” he said. He emphasized that the banking and financial sectors remain secure and that online transactions are safe.
Bank Rakyat issued a statement on November 7, attributing the access disruption to a technical issue in a third-party service provider’s system. The bank assured customers that its core banking systems and operations continued to run as usual, while personal data, banking information, and savings remained safe and unaffected. The bank blocked access to the affected server and redirected users to the i-Rakyat website, which it fully owns. Customers were advised to continue banking through alternative official channels, including the iRakyat mobile application, BRICK, QR2E, and the i-bizRAKYAT business banking portal.
The distinction between a compromised public website and a breach of core banking infrastructure is significant. As noted in security analysis, a compromised public website does not automatically mean that hackers have access to customer accounts or the ability to transfer funds. While the attacker claimed to have retrieved a sample of data, neither the bank nor the government has confirmed that internal databases were breached. A separate report from a Malaysian technology publication noted that the defacement included the online banking login page, but the bank’s official stance remains that the core systems were insulated from the intrusion.
In response to the incident, Prime Minister Datuk Seri Anwar Ibrahim ordered the National Security Council (MKN) to review potential security threats to various national infrastructure facilities, particularly hybrid threats. Fahmi stated that this exercise, ordered as early as the beginning of last week, involves examining internet infrastructure, websites, and databases to ensure the continued protection of the country’s digital assets. At a Cabinet meeting on Friday, the Prime Minister called for a more thorough review of cybersecurity across all government assets, banking institutions, and government-linked companies (GLCs).
The incident has sparked public debate on social media regarding the resilience of Malaysia’s digital financial infrastructure. While some users expressed concern about the rising frequency of cyberattacks, the government maintains that the current safeguards are holding. Fahmi’s comments come as Malaysia seeks to retain its seat on the ITU council for a three-year term, highlighting the nation’s ongoing engagement with global digital governance standards.
The immediate next step is the completion of the National Security Council’s review of cybersecurity across critical digital infrastructure. This assessment aims to identify vulnerabilities in third-party service providers and ensure that similar incidents do not escalate into broader security breaches.
One Comment