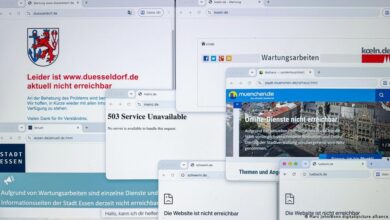
The scale of the threat was underscored by cybersecurity companies, which reported that millions of attempts to attack websites have already been recorded since the issue with the programming language was publicly revealed. This rapid surge in malicious activity indicates that the vulnerability is being actively probed by automated botnets and targeted attackers, creating a high-pressure environment for IT teams tasked with securing their digital assets.
PHP (Hypertext Preprocessor) remains a foundational technology in the web development ecosystem. While the specific technical mechanics of this particular flaw were not detailed in the initial reporting, the severity of the reaction from global organizations suggests a high-priority issue. In typical scenarios involving such language-level vulnerabilities, the risk often involves unauthorized access to server resources or the execution of malicious code, which can lead to the compromise of entire web applications.
The immediate impact has been a visible degradation of internet reliability. As organizations prioritize security over availability, many have chosen to take their websites offline temporarily. This precautionary measure, while effective in preventing exploitation, results in a significant loss of service for users and businesses. For governments, the downtime of public portals can impede citizen services, while for commercial entities, it represents a direct loss of revenue and customer trust.
The situation highlights the inherent fragility of the global digital infrastructure when reliant on shared, open-source components. When a flaw is identified in a core technology like PHP, the remediation process is not isolated to a single company but becomes a collective, global effort. The speed at which millions of attack attempts are logged after a disclosure suggests that exploit code or detection signatures are circulating widely, reducing the window of opportunity for organizations to patch their systems before being targeted.
Cybersecurity experts have emphasized the importance of immediate action, urging system administrators and developers to apply the necessary updates as soon as they are available. The distinction between a theoretical vulnerability and an actively exploited one is critical here; the reported millions of attempts confirm that this is no longer a hypothetical risk but a live threat. The potential consequences of a successful exploit include not just data breaches, but the complete takeover of web servers, which could be used to launch further attacks against other systems or to disrupt services on a massive scale.
The incident serves as a stark reminder of the ongoing arms race between security researchers and cybercriminals. As more sophisticated tools become available to attackers, the burden on defenders to maintain up-to-date and secure systems increases. The global nature of the disruption underscores the interconnectedness of the internet, where a single flaw in a widely adopted technology can have cascading effects across borders and industries.
While the immediate crisis focuses on patching and recovery, the long-term implications for web security policy and software maintenance practices are likely to be significant. Organizations may face increased scrutiny regarding their incident response plans and vulnerability management processes. The event also underscores the critical role of timely disclosure and the availability of reliable patches in mitigating such widespread threats.
As of the latest reports, the primary focus remains on the urgent application of fixes to prevent further compromise. The next critical step for affected entities is to verify that all instances of PHP have been updated and to monitor for any signs of prior intrusion. The resolution of this incident will depend on the speed and thoroughness of the global remediation effort, as well as the continued vigilance of cybersecurity teams in detecting and blocking ongoing attack attempts.