The technical nature of the breach highlights a specific vulnerability in modern retail infrastructure: the integration of Internet of Things (IoT) devices with physical supply chains. According to Danilo Radenza, chief executive of Coop Radenza, a careful screening revealed that the attack targeted the remote control mechanisms for refrigeration units. While Radenza stated that “there is no further damage” beyond the physical loss of food, the incident underscores how cyber threats can translate into physical consequences, disrupting operations and causing direct financial loss. The attack was successful because it manipulated the environmental controls of the stores, a system that relies on remote access and connectivity to manage equipment across multiple locations.
This incident in Italy is part of a wider pattern of cyberattacks hitting the European supermarket sector. The same wave of disruptions affected approximately one hundred supermarkets in Sweden, Belgium, Luxembourg, Estonia, and Ireland. In all affected locations, the methodology appears consistent: refrigeration temperatures were pushed to critical levels, leading to the spoilage of inventory. Just days earlier, on October 12, a similar cyberattack struck the main supermarket chains in France, resulting in losses estimated in the millions of euros. Although no group has yet claimed responsibility for these coordinated incidents, officials and analysts note that there appear to be few doubts that the attacks are connected. The European Union has officially described the situation as “highly worrying,” signaling a recognition that the retail sector is becoming a primary target for state-sponsored or organized criminal cyber operations.

In response to the Italian incidents, the National Cybersecurity Agency (Acn) has intervened, reporting that it has also detected an attack against a company in Emilia that produces frozen foods and received reports concerning a Tuscan company in the collective catering sector. The Agency’s involvement marks a shift from corporate-level response to national-level security coordination. Acn has issued urgent recommendations to the sector, advising companies to check whether their control and remote assistance systems are exposed to the Internet. The agency specifically highlighted the need to strengthen remote access via Virtual Private Networks (VPNs), implement multi-factor authentication, review privileged accounts, and update or replace devices that are no longer supported by their manufacturers. These technical measures address the root causes of such vulnerabilities: outdated hardware and insecure remote access protocols that allow attackers to manipulate physical systems from a distance.
The commercial and regulatory fallout in Italy is substantial. The postal police are currently reconstructing the origin and scale of the attacks to determine if there are direct links to the incidents in other European countries. To address the crisis, Palazzo Chigi has convened a high-level meeting involving the Director of the National Cybersecurity Agency and the heads of the intelligence agencies, coordinated by Alfredo Mantovano, the undersecretary to the prime minister’s office. Additionally, the Parliamentary Committee for the Security of the Republic (Copasir) is scheduled to request information from the government on Tuesday. A further meeting is set to take place between the Acn, sector federations, and major national retail companies to discuss mitigation strategies and share threat intelligence.
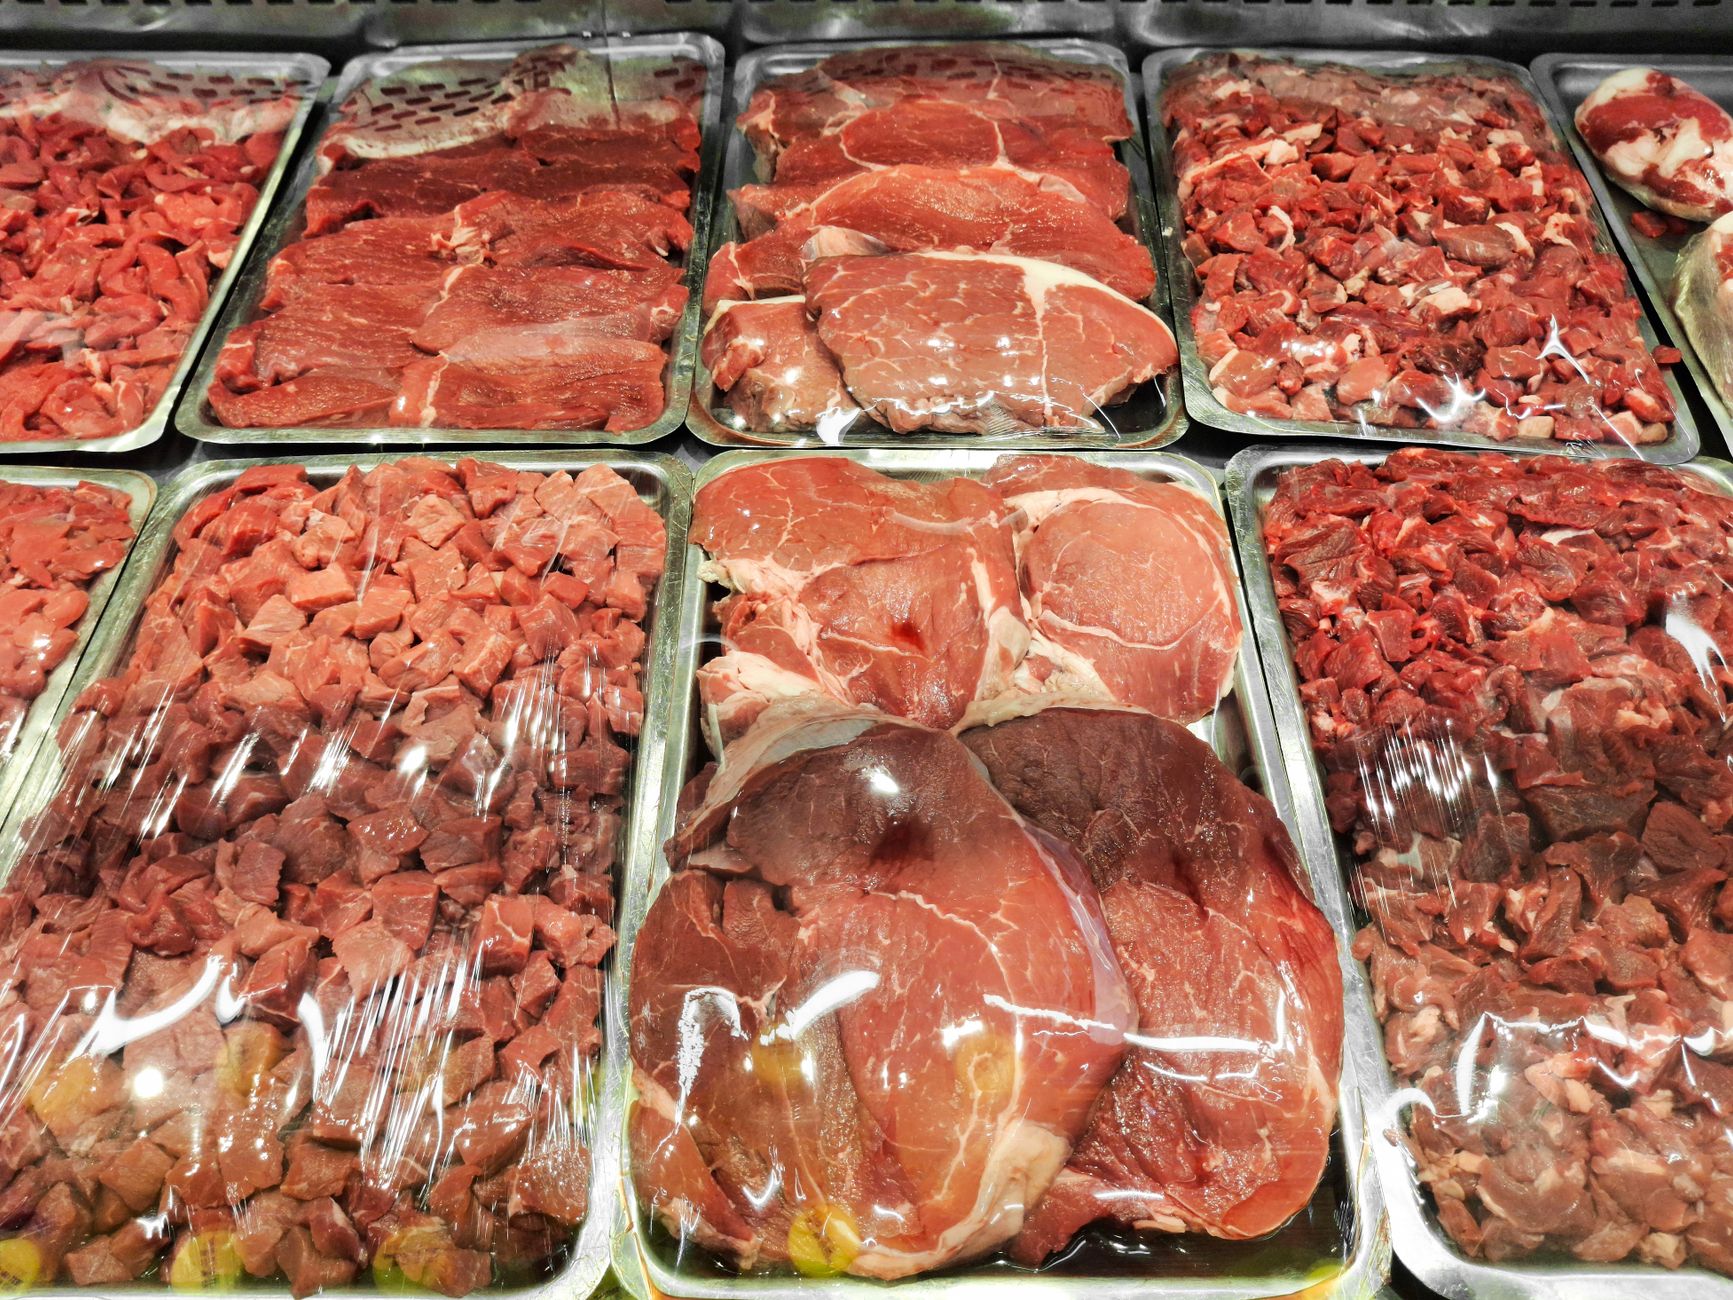
For retailers, the immediate focus is on calculating damages and restoring security. Radenza confirmed that in some cases, the technical issues have already been fixed, but the financial impact of the discarded food remains under assessment. The incident serves as a stark reminder that cybersecurity is no longer just about protecting data, but about preserving the physical integrity of the supply chain. As the postal police continue their investigation into the links between Italy and the broader European attacks, the retail sector faces a difficult question: how to secure legacy hardware against sophisticated cyber threats while maintaining operational efficiency. The upcoming government meetings and the Acn’s ongoing investigation will determine whether Italy can isolate the threat or if the coordinated nature of the attacks will lead to a more comprehensive overhaul of retail cybersecurity standards across the continent.