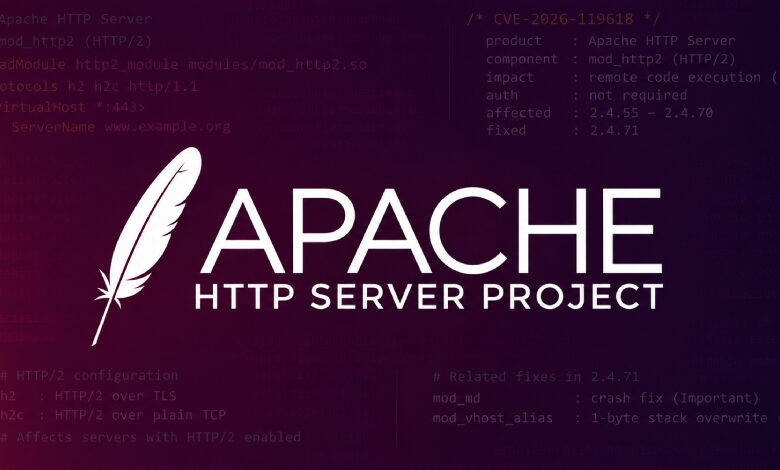
The root cause is a race condition in the assign_headers() function, where improper synchronization of concurrent execution using shared resources leads to heap memory corruption. This corruption can be leveraged to achieve remote code execution (RCE), granting the attacker full control of the server process. Red Hat, which ships the server in Red Hat Enterprise Linux, rates the flaw 9.8 out of 10 on the CVSS scale. The vendor’s assessment states that “public research has demonstrated a reliable exploit” against servers in default configuration with mod_http2 enabled, though it did not link the specific research. Conversely, security firm Wiz reported that no exploit code is available and no exploitation in the wild has been reported as of the publication of its analysis.
The practical impact is significant for cloud infrastructure. Wiz data indicates that 64% of cloud environments contain resources vulnerable to this flaw, and 51% of those environments have publicly exposed instances. However, these figures do not account for specific configurations, such as whether HTTP/2 is enabled. The vulnerability only affects servers where the Protocols directive includes h2 (HTTP/2 over TLS) or h2c (HTTP/2 over plain TCP). Administrators must check both server-wide settings and individual virtual host configurations to determine exposure.
Remediation is straightforward for standard users: upgrade to Apache HTTP Server version 2.4.71. This release is recommended over all previous versions. For users of the standalone mod_h2 module on GitHub, no fixed release has been published; the repository has been read-only since its archival on June 9, with the last release being 2.0.42, which is affected. Admins who cannot immediately update are advised to disable HTTP/2 by removing h2 and h2c from the Protocols directive, leaving only http/1.1. Red Hat has already shipped fixes for Red Hat Enterprise Linux 9 and 10, rating the flaw as “Important” for those specific distributions due to memory allocator differences that complicate exploitation.
Version 2.4.71 also addresses two additional bugs: CVE-2026-106023, a NULL pointer dereference in mod_md rated “important,” and CVE-2026-109163, a one-byte buffer overwrite in mod_vhost_alias rated “low.” The CVE is not currently listed in the CISA Known Exploited Vulnerabilities (KEV) catalog. Organizations should prioritize patching to mitigate the risk of unauthenticated remote code execution in their web infrastructure.