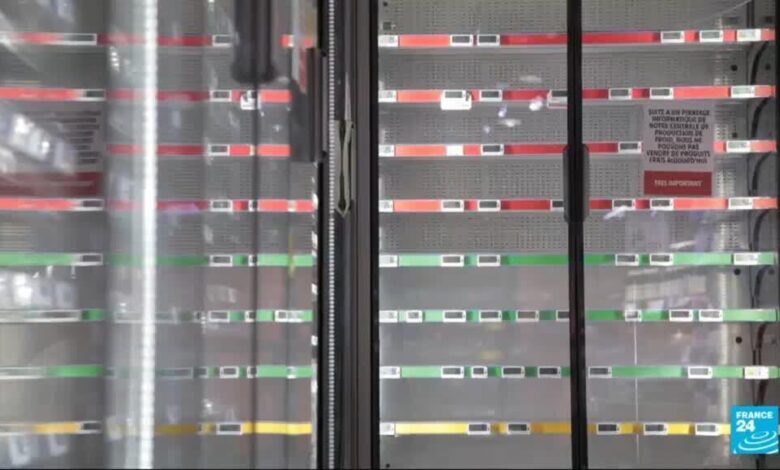
The incident represents a notable shift in the landscape of cyber warfare, where attacks are increasingly moving beyond traditional digital targets such as data servers or financial networks to directly impact physical infrastructure. By compromising the control systems of supermarket fridges, the attackers demonstrated the potential for cyber operations to have immediate, tangible consequences for public health and supply chains. While the specific technical method of the intrusion has not been detailed in the initial reports, the ability to affect the operational status of hundreds of units simultaneously suggests a sophisticated command-and-control structure or a widespread vulnerability in the connected devices used by major retail chains.
France’s attribution of the attack to Iran adds a layer of geopolitical complexity to what would otherwise be a domestic cybersecurity issue. If the attribution is accurate, it signals a willingness by state actors to target civilian economic infrastructure in Europe as a form of asymmetric pressure. The EU’s pledge of a “united response” indicates that member states are coordinating their defensive and potentially retaliatory measures. This coordination is critical in the current climate, where fragmented national responses have often failed to deter state-sponsored cyber activities. The response could range from diplomatic condemnations and sanctions to coordinated cyber-defense exercises and, in some frameworks, the authorization of reciprocal cyber operations.
From a technical and regulatory standpoint, the incident highlights the growing vulnerability of the Internet of Things (IoT) in critical sectors. Commercial refrigeration units, particularly those in large retail environments, are increasingly connected to cloud-based monitoring platforms to track temperature, energy usage, and maintenance needs. These connections, while beneficial for operational efficiency, expand the attack surface for malicious actors. The attack underscores the urgency for stricter security standards in the development and deployment of connected industrial and commercial hardware. Regulators and industry bodies may face increased pressure to enforce robust cybersecurity protocols for devices that, while not traditionally classified as “critical infrastructure” in the same vein as power grids or water treatment plants, are essential to food safety and public health.
The broader implications of this event extend to the concept of “cyber-physical” threats. Unlike data theft or ransomware, which primarily affects digital assets and financial stability, attacks on physical infrastructure can result in immediate physical damage, waste of perishable goods, and potential health hazards. This blurring of the line between digital and physical security challenges existing defense frameworks, which are often designed to protect data integrity and availability rather than physical continuity. Companies in the retail and logistics sectors will likely reassess their supply chain security, potentially accelerating the adoption of air-gapped systems or more rigorous network segmentation for critical operational technology.
For businesses, the incident serves as a stark reminder that cybersecurity is no longer just an IT issue but a core operational risk. Retailers and food distributors must ensure that their connected devices are patched, monitored, and isolated from general corporate networks where possible. The event also raises questions about the resilience of global supply chains to state-sponsored cyber disruptions. As nations become more willing to use cyber capabilities to exert political influence, the stability of everyday commercial operations becomes a matter of national security.
The EU’s response will be closely watched as a precedent for how the bloc handles cyberattacks attributed to foreign state actors that target civilian infrastructure. The coming days will likely see further technical investigations, diplomatic channels opened or closed, and potential policy adjustments to address the vulnerabilities exposed by this incident. The situation remains fluid, with the full extent of the damage and the precise vector of the attack still being assessed by European cybersecurity agencies.
The next critical development will be the specific nature of the EU’s “united response,” which is expected to be detailed in the coming days, along with any further technical findings from the French investigation into the scope and method of the Iranian-linked intrusion.